USPTO serial 97361962
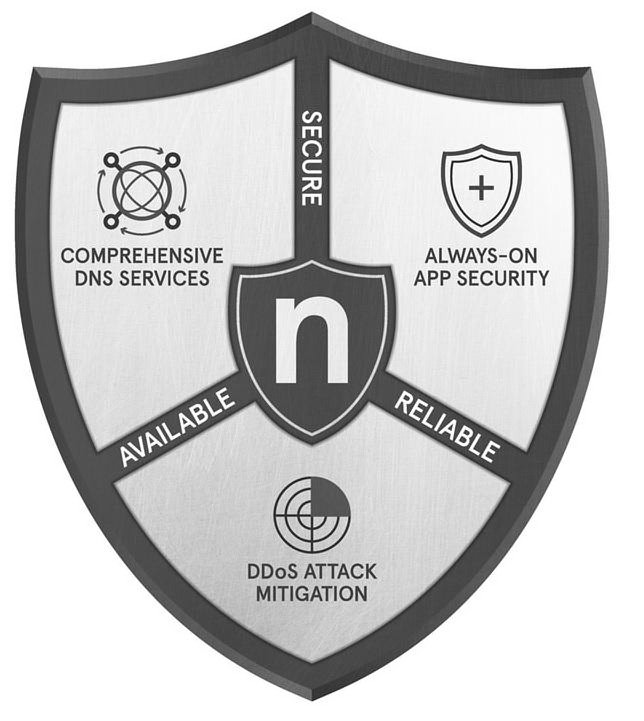
N SECURE AVAILABLE RELIABLE COMPREHENSIVE DNS SERVICES ALWAYS-ON APP SECURITY DDOS ATTACK MITIGATION
Reviewed by CopyMark Law Group
Status 606
- Filing date
- Status date
- Registration date
- —
- Examiner
- DANG, BAO-NGOC K
- Law office
- INTENT TO USE SECTION
What this means
This page summarizes the public USPTO record for this serial number, including owners, goods and services, and prosecution history.
Need help with N SECURE AVAILABLE RELIABLE COMPREHENSIVE DNS SERVICES ALWAYS-ON APP SECURITY DDOS ATTACK MITIGATION?
If you own this trademark, we can monitor new filings and help with USPTO deadlines. If you do not, we can file a new U.S. application.
Current trademark owner
Monitor this mark, or talk with CopyMark about this registration.
Not the owner?
File a new U.S. trademark application, or speak with our attorneys.
Owner
Attorney of record
The USPTO lists this attorney as the applicant's representative for correspondence on this application.
Peter J. Riebling
Peter J. Riebling RIEBLING IP, PLLC1717 Pennsylvania Avenue, N.W.Suite 1025Washington, DC 20006Goods and services
| Class | Description | Status | First use |
|---|---|---|---|
| 009 | Computer hardware and downloadable software for use in assessing, analyzing and making inferences with respect to detecting, mitigating and resolving Internet traffic threats, assessing intelligence data, and analyzing and making inferences regarding end user's Internet traffic to determine how such traffic should be handled; Downloadable software for use in providing statistical analysis of business functions; downloadable software for providing demographic information and data concerning the geographic location of internet access devices used by consumers, the geographic locations of consumers, the connection speed and method by which consumers are accessing the internet, and the specific types of devices used by consumers to access the internet; Downloadable software for providing access to and creating databases featuring IT information about Internet Protocol addresses in the nature of the user's location, Internet service provider, organization, connection type, user type and other data associated with specific Internet Protocol addresses; Downloadable software for providing access to technology that allows users to determine the location, Internet service provider, organization, connection type, user type, and other data associated with specific Internet Protocol addresses; Downloadable software for providing (IP) address verification services; Downloadable software for providing access to and creating databases featuring the location, internet service provider and organization associated with specific internet addresses; Downloadable software for providing identification of website visitor geographical location by using IP address; Downloadable software for providing identification of the location and other characteristics of Internet users for a wide range of applications including content personalization, fraud detection, ad targeting, traffic analysis, compliance, geo-targeting, geofencing and digital rights management; Downloadable software for providing internet directory services, namely, recursive domain name server (DNS) services; Downloadable software for identification and tracking of IP addresses and ranking or scoring them according to their reputation; Downloadable software for use in detecting, mitigating and resolving Internet traffic threats and for use in providing intelligence data to assess, analyze and make inferences regarding an end user's Internet traffic, to make determinations as to how such traffic should be handled; Downloadable software for use in detecting, mitigating and resolving Internet traffic security threats; Downloadable software for use in compiling computer security threat intelligence data to assess, analyze and make inferences regarding an end user's Internet traffic and to make determinations as to how such traffic should be handled; Downloadable software for providing machine readable threat intelligence (MRTI) information and data to help determine if incoming Internet traffic is malicious and to discover associations among threat actors to track and block their activity | ACTIVE | — |
| 042 | Providing on-line searchable databases featuring IT information about Internet Protocol addresses in the nature of the user's location, Internet service provider, organization, connection type, user type and other data associated with specific Internet Protocol addresses; computer services, namely, providing an interactive web site featuring technology that allows users to determine the location, Internet service provider, organization, connection type, user type, and other data associated with specific Internet Protocol addresses; Internet Protocol (IP) address verification services; providing online searchable databases featuring the location, internet service provider and organization associated with specific internet addresses; providing an interactive website featuring technology that enables user to identify the geographical location of website visitors by IP address, for a wide range of applications including, fraud detection, compliance, geo-targeting, geo-fencing and digital rights management; computer security threat analysis for protecting data by providing threat analysis data to assess, analyze and make inferences regarding an end user's Internet traffic and to make determinations as to how such traffic should be handled; Network security and threat detection, mitigation and resolution services, namely, providing temporary use of non-downloadable cloud-based software for cleaning, scrubbing and filtering of malicious internet and network traffic; electronic monitoring and reporting of servers, networks, network systems, network data, network information, data packets, and internet protocol traffic using computers for security purposes and providing related reports featuring suspicious and abnormal patterns and anomalies of networks, system activity reports, and event notification alerts; Providing temporary use of on-line non-downloadable software for use in detecting, identifying, intercepting, capturing, quarantining and preventing online threats; providing temporary use of on-line non-downloadable software for use in preventing access to malicious websites and online threats; providing temporary use of online non-downloadable software for use in blocking unwanted and inappropriate internet and network traffic, for mitigating against and defending networks and websites from distributed denial of service (DDoS) attacks and implementation of countermeasures to limit exposure from such attacks and protect a website's uptime; providing temporary use of online non-downloadable software for use in providing bot management, mitigation, protection and guarding against online and software threats; Computer security services, namely, providing temporary use of non-downloadable cloud-based firewall software that monitors and filters DNS queries to prevent and block computer network users from accessing unwanted and inappropriate content and from accessing custom-designated third-party websites or preventing access to malicious websites or online threats; Providing temporary use of on-line non-downloadable cloud computing software for resolving domain name system errors and discrepancies; computer security threat analysis for protecting data by protecting online businesses from the effects of DNS-based DDoS attacks and other threats; computer security threat analysis for protecting data through identification, blocking and mitigating targeted online threats such as malware, ransom ware, phishing, DNS data exfiltration, and advanced zero-day attacks; providing temporary use of on-line non-downloadable website software application and API security and threat detection, mitigation and resolution services, namely, a web application firewall (WAF) that cleans, scrubs and filters malicious attacks against website software applications and application programming interface (API's); Computer services, namely, monitoring and reporting on the performance, availability, and errors of web sites of others and API's for security purposes and providing related reports featuring suspicious and abnormal patterns, anomalies and activities; providing temporary use of online downloadable software for use in detecting, identifying, intercepting, capturing, quarantining and preventing threats to website software applications and API's; computer security services, namely, providing temporary use of online non-downloadable software for use restricting unauthorized network access by preventing access to malicious websites and online threats, blocking unwanted and inappropriate interactions with website software applications and API's, mitigating against and defending attacks against website software applications and API's and implementation of countermeasures to limit exposure from such attacks and protect a website's uptime; DNS resolver services that make DNS queries faster and more secure for faster and more private browsing of the Internet, namely, providing temporary use of online non-downloadable computer software for use in securing and speeding internet browsing capacity; global DNS resolution service, namely, computer code conversion for others; providing temporary use of non-downloadable software for use in providing an internet directory comprising recursive domain name server (DNS) services | ACTIVE | — |
Related trademarks
CopyMark links this record to cited §2(d) serials, the owner's other marks, Nice classes, similar mark names, and recently changed USPTO applications.
- Other trademarks owned by Security Services, LLC
- Other trademarks owned by Security Services, LLC
- Other trademarks owned by VERCARA, LLC
- Other trademarks in Class 009
- Other trademarks in Class 042
- Similar marks named N SECURE AVAILABLE RELIABLE COMPREHENSIVE DNS SERVICES ALWAYS-ON APP SECURITY DDOS ATTACK MITIGATION
- Prosecution event MAB6 explained
- Recently changed USPTO trademarks
- Recently filed trademarks
- Browse all trademark records
Prosecution history
| Date | Code | Event | What it means |
|---|---|---|---|
| Jan 22, 2024 | MAB6 | ABANDONMENT NOTICE E-MAILED - NO USE STATEMENT FILED | The intent-to-use application was abandoned because no acceptable Statement of Use (or valid extension) was filed before the Notice of Allowance deadline expired. The application is dead unless revived within a limited window. |
| Jan 22, 2024 | ABN6 | ABANDONMENT - NO USE STATEMENT FILED | The intent-to-use application was abandoned because no acceptable Statement of Use (or valid extension) was filed before the Notice of Allowance deadline expired. The application is dead unless revived within a limited window. |
| Nov 6, 2023 | TCCA | TEAS CHANGE OF CORRESPONDENCE RECEIVED | — |
| Nov 6, 2023 | ARAA | ATTORNEY/DOM.REP.REVOKED AND/OR APPOINTED | This event means the applicant filed a response to a USPTO Office Action — typically arguments, amendments, or evidence addressing the examiner's objections. The USPTO will review the response and either allow the mark to proceed or issue another action. |
| Nov 6, 2023 | REAP | TEAS REVOKE/APP/CHANGE ADDR OF ATTY/DOM REP RECEIVED | — |
| Nov 6, 2023 | CHAN | APPLICANT/CORRESPONDENCE CHANGES (NON-RESPONSIVE) ENTERED | — |
| Nov 6, 2023 | COAR | TEAS CHANGE OF OWNER ADDRESS RECEIVED | — |
| Jul 1, 2023 | TCCA | TEAS CHANGE OF CORRESPONDENCE RECEIVED | — |
| Jul 1, 2023 | ARAA | ATTORNEY/DOM.REP.REVOKED AND/OR APPOINTED | This event means the applicant filed a response to a USPTO Office Action — typically arguments, amendments, or evidence addressing the examiner's objections. The USPTO will review the response and either allow the mark to proceed or issue another action. |
| Jul 1, 2023 | REAP | TEAS REVOKE/APP/CHANGE ADDR OF ATTY/DOM REP RECEIVED | — |
| Jul 1, 2023 | CHAN | APPLICANT/CORRESPONDENCE CHANGES (NON-RESPONSIVE) ENTERED | — |
| Jul 1, 2023 | COAR | TEAS CHANGE OF OWNER ADDRESS RECEIVED | — |
| Jun 20, 2023 | NOAM | NOA E-MAILED - SOU REQUIRED FROM APPLICANT | A Notice of Allowance means your intent-to-use application cleared examination and opposition but is not registered yet. You must file a Statement of Use showing the mark in commerce, or request an extension, before the deadline — usually six months from the notice date. |
| May 3, 2023 | ASGN | AUTOMATIC UPDATE OF ASSIGNMENT OF OWNERSHIP | — |
| Apr 25, 2023 | NPUB | OFFICIAL GAZETTE PUBLICATION CONFIRMATION E-MAILED | — |
| Apr 25, 2023 | PUBO | PUBLISHED FOR OPPOSITION | Your mark was published in the USPTO Official Gazette for a 30-day opposition window. During that period, third parties who believe they would be harmed can file an opposition. If no opposition is filed, prosecution usually continues toward registration or a Notice of Allowance. |
| Apr 5, 2023 | NONP | NOTIFICATION OF NOTICE OF PUBLICATION E-MAILED | — |
| Mar 24, 2023 | CHAN | APPLICANT/CORRESPONDENCE CHANGES (NON-RESPONSIVE) ENTERED | — |
| Mar 24, 2023 | TCCA | TEAS CHANGE OF CORRESPONDENCE RECEIVED | — |
| Mar 24, 2023 | ARAA | ATTORNEY/DOM.REP.REVOKED AND/OR APPOINTED | This event means the applicant filed a response to a USPTO Office Action — typically arguments, amendments, or evidence addressing the examiner's objections. The USPTO will review the response and either allow the mark to proceed or issue another action. |
| Mar 24, 2023 | REAP | TEAS REVOKE/APP/CHANGE ADDR OF ATTY/DOM REP RECEIVED | — |
| Mar 24, 2023 | COAR | TEAS CHANGE OF OWNER ADDRESS RECEIVED | — |
| Mar 22, 2023 | CNSA | APPROVED FOR PUB - PRINCIPAL REGISTER | — |
| Mar 22, 2023 | XAEC | EXAMINER'S AMENDMENT ENTERED | — |
| Mar 22, 2023 | GNEN | NOTIFICATION OF EXAMINERS AMENDMENT E-MAILED | — |
| Mar 22, 2023 | GNEA | EXAMINERS AMENDMENT E-MAILED | — |
| Mar 22, 2023 | CNEA | EXAMINERS AMENDMENT -WRITTEN | — |
| Mar 21, 2023 | XAEC | EXAMINER'S AMENDMENT ENTERED | — |
| Mar 21, 2023 | GNEN | NOTIFICATION OF EXAMINERS AMENDMENT E-MAILED | — |
| Mar 21, 2023 | GNEA | EXAMINERS AMENDMENT E-MAILED | — |
| Mar 21, 2023 | CNEA | EXAMINERS AMENDMENT -WRITTEN | — |
| Mar 1, 2023 | TEME | TEAS/EMAIL CORRESPONDENCE ENTERED | — |
| Mar 1, 2023 | CRFA | CORRESPONDENCE RECEIVED IN LAW OFFICE | — |
| Mar 1, 2023 | TROA | TEAS RESPONSE TO OFFICE ACTION RECEIVED | This event means the applicant filed a response to a USPTO Office Action — typically arguments, amendments, or evidence addressing the examiner's objections. The USPTO will review the response and either allow the mark to proceed or issue another action. |
| Jan 6, 2023 | GNRN | NOTIFICATION OF NON-FINAL ACTION E-MAILED | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Jan 6, 2023 | GNRT | NON-FINAL ACTION E-MAILED | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Jan 6, 2023 | CNRT | NON-FINAL ACTION WRITTEN | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Dec 8, 2022 | TEME | TEAS/EMAIL CORRESPONDENCE ENTERED | — |
| Dec 8, 2022 | CRFA | CORRESPONDENCE RECEIVED IN LAW OFFICE | — |
| Dec 8, 2022 | TROA | TEAS RESPONSE TO OFFICE ACTION RECEIVED | This event means the applicant filed a response to a USPTO Office Action — typically arguments, amendments, or evidence addressing the examiner's objections. The USPTO will review the response and either allow the mark to proceed or issue another action. |
| Jun 8, 2022 | GNRN | NOTIFICATION OF NON-FINAL ACTION E-MAILED | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Jun 8, 2022 | GNRT | NON-FINAL ACTION E-MAILED | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Jun 8, 2022 | CNRT | NON-FINAL ACTION WRITTEN | A non-final Office Action means the USPTO examining attorney has raised at least one issue with your trademark application but has not made a final decision. You usually have three months to respond with arguments, amendments, or evidence. Missing the deadline can abandon the application. |
| Jun 2, 2022 | DOCK | ASSIGNED TO EXAMINER | — |
| Apr 20, 2022 | MDSC | NOTICE OF DESIGN SEARCH CODE E-MAILED | — |
| Apr 19, 2022 | NWOS | NEW APPLICATION OFFICE SUPPLIED DATA ENTERED | — |
| Apr 16, 2022 | NWAP | NEW APPLICATION ENTERED | — |